Your AI assistant shipped a vulnerability.
Vergate catches it first.
RLS misconfigurations, exposed API keys, broken auth, missing security headers — the mistakes AI coding assistants make silently. Scan from Cursor, Claude Code, Lovable or any editor, then paste one copy-ready fix prompt.
Free scan · 50+ checks No signup required
Built for code written in
Six ways AI-generated code
breaks in production.
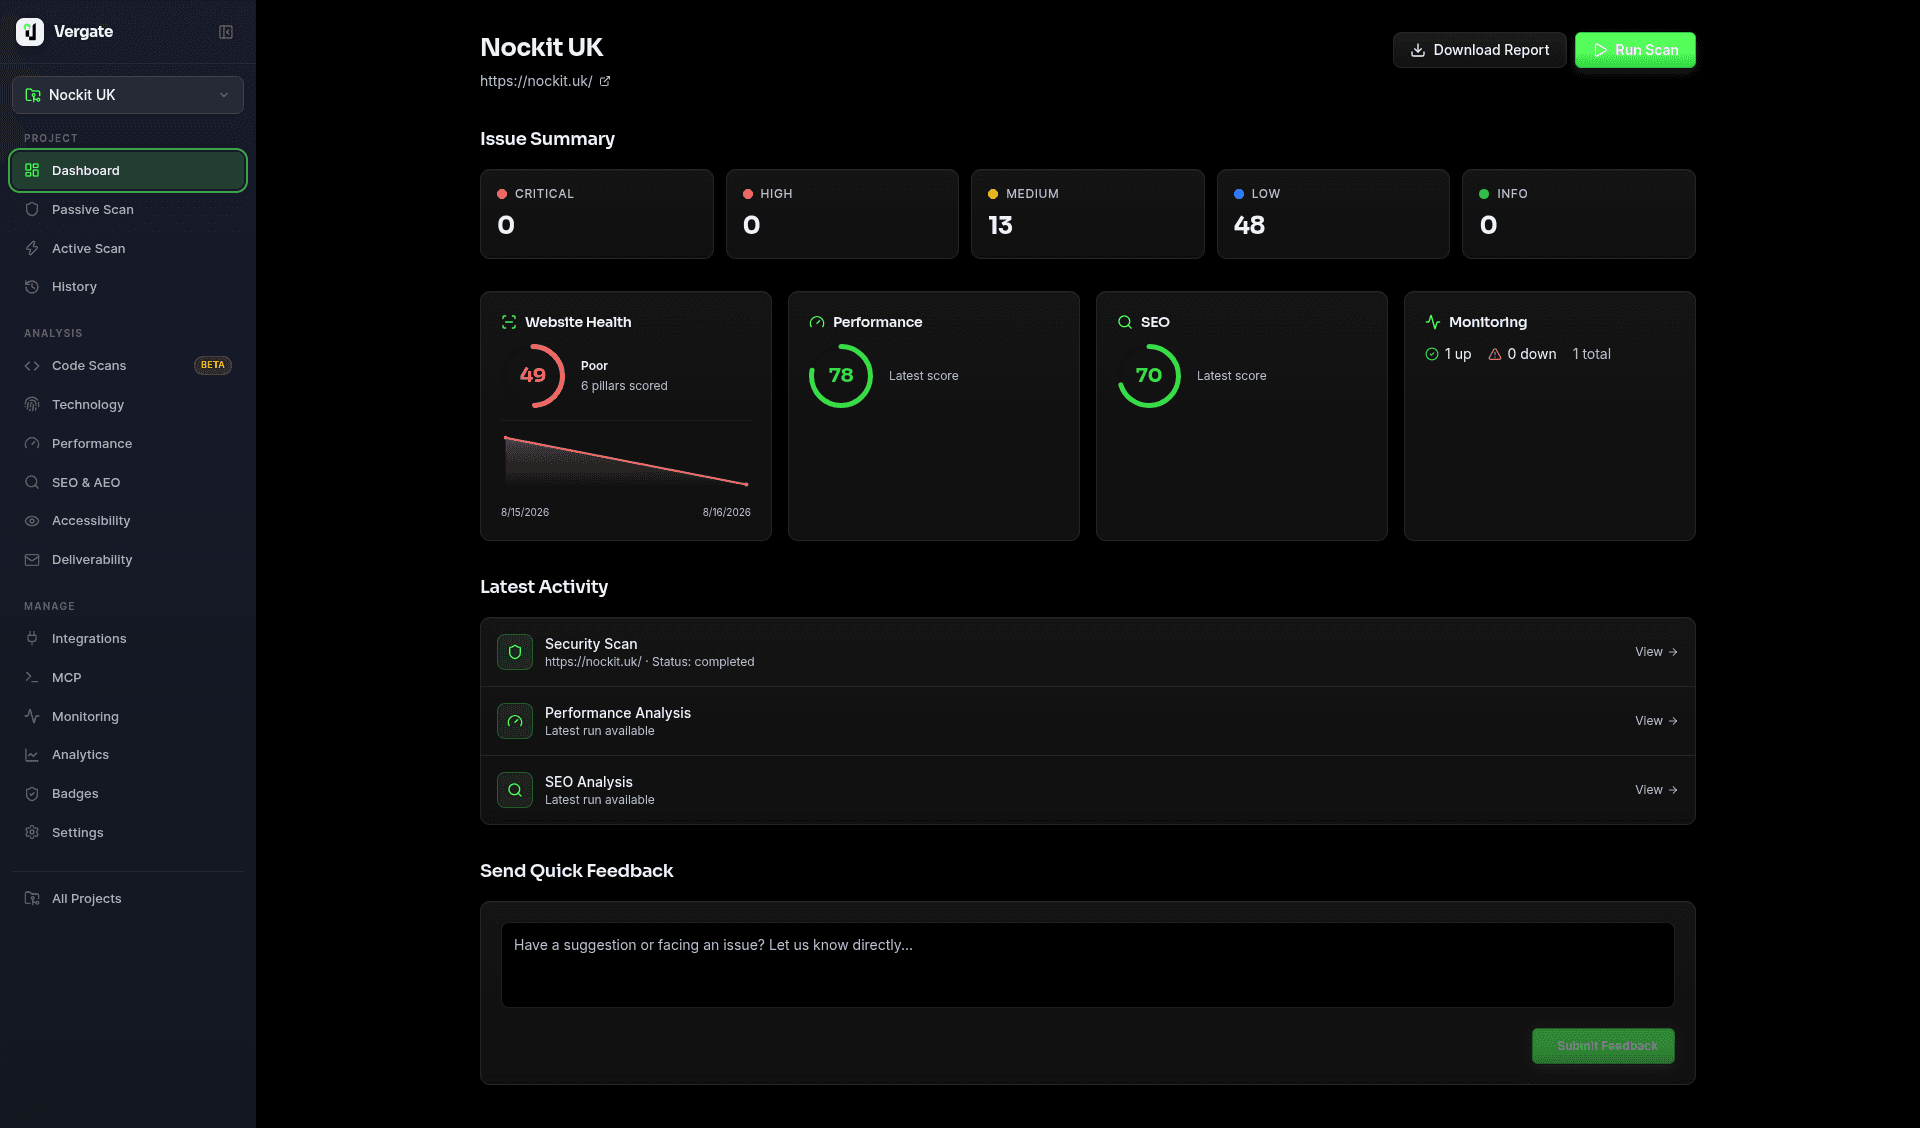
AI writes the feature in seconds — and the misconfiguration too. One scan checks all six, with a health score that tells you where to start.
Audit → find it · Fix → ship the fix · Monitor → catch regressions · Understand → know your score
Everything that can quietly
break your website
Six pillars. One scan. Evidence for every finding.
Catch the mistakes AI coding assistants make
Exposed API keys, missing auth, open RLS policies, permissive CORS, weak cookies — the quiet failures a generated codebase ships with.
Find SQL injection, XSS, and open redirects
Active DAST scanning probes your endpoints for injection vulnerabilities that passive checks can't find.
Catch regressions before users notice them
Core Web Vitals, bundle sizes, caching, and third-party impact — rated against thresholds so you know what to fix.
Get cited by AI chatbots, not just ranked by Google
Meta tags, structured data, sitemap — plus GPTBot, ClaudeBot, and PerplexityBot access checks for AI-answer-engine optimization.
Find the WCAG failures that exclude real users
axe-core runs WCAG 2.1 AA checks. Violations grouped by impact with CSS selectors you can act on immediately.
Know when your site goes down instead of discovering it from a customer
Configurable uptime monitoring with alerts via email, Slack, Discord, or Telegram.
Stop your emails from landing in spam
SPF, DKIM, DMARC, MX, MTA-STS, DNSSEC — 9 DNS checks that find the one misconfig killing your inbox placement.
Know exactly what your stack is running
50+ detectors plus WhatWeb identify frameworks, hosting, CDN, analytics, auth, and payment integrations on any site.
Evidence-backed findings you can verify
Every finding includes raw evidence. Reports are signed and tamper-evident. We scan our own site with the same engine.
Your coding agent scans, you paste the fix
Vergate ships as an MCP server — Cursor, Claude Code, WindSurf, Lovable and other AI IDEs call it like any other tool. One prompt is enough: scan example.com and fix what it finds. The agent runs the scan, reads the report, and applies the fixes itself.
Your stack. Your workflow. Already supported.
From URL to understanding
Paste a URL. Get a scored report. Fix it. Ship.
Audit
Paste a URL — or ask your AI editor via MCP — and Vergate runs 50+ security, performance, SEO, accessibility, and reliability checks in seconds.
Fix
Every finding includes evidence and a copy-paste prompt. Drop it into Cursor or Claude Code and the agent applies the fix itself.
Monitor
Set up ongoing checks. Get alerts when something breaks or regresses.
Understand
A single health score with six pillars — so you always know where you stand.
It found 8 security issues on our own site.
We ran our own scanner against vergate.dev. It flagged missing security headers, exposed configuration, and an HSTS gap. We fixed every one, then documented exactly what happened — including how Vercel's bot protection confused our own scanner into thinking the site was running Astro.
Pricing that scales with your projects
Start free. Upgrade when you need more projects, faster alerts, or team features.
Free
Try Vergate with no commitment
- 1 project
- 3 passive scans per month
- Security, performance, SEO, accessibility checks
- AI fix prompts for every finding
- MCP support for Claude Code, Cursor, Windsurf and VS Code
- API access
Starter
For your side projects
- Monitor up to 3 projects — alerted within ~15 min
- Passive security scans catch misconfigurations before they ship
- Performance checks flag slow pages before users bounce
- SEO & AEO checks keep you visible in search and AI answers
- MCP support for Claude Code, Cursor, Windsurf and VS Code
- Community support via email
Pro
Run your SaaS with confidence
- Monitor up to 12 projects — alerted within ~5 min
- Active vulnerability scans catch SQLi, XSS, and open redirects
- Performance checks catch regressions before every release
- SEO & AEO checks across every deployment
- CI/CD integration for automated scanning
- MCP support for Claude Code, Cursor, Windsurf and VS Code
- Priority email support
Max
Run your business at scale
- Monitor unlimited projects — alerted within ~1 min
- Priority scanning queues — results in seconds, not minutes
- Security scanning at scale across your entire fleet
- Performance monitoring at scale
- SEO & AEO checks across every domain
- MCP support for Claude Code, Cursor, Windsurf and VS Code
- Slack / Teams integration for instant alerts
- SSO (SAML / OIDC) for your team
- Dedicated support + SLA